Fake IT worker crime story or ordinary remote hire what is better for explaining how North Korea gets hired by American companies
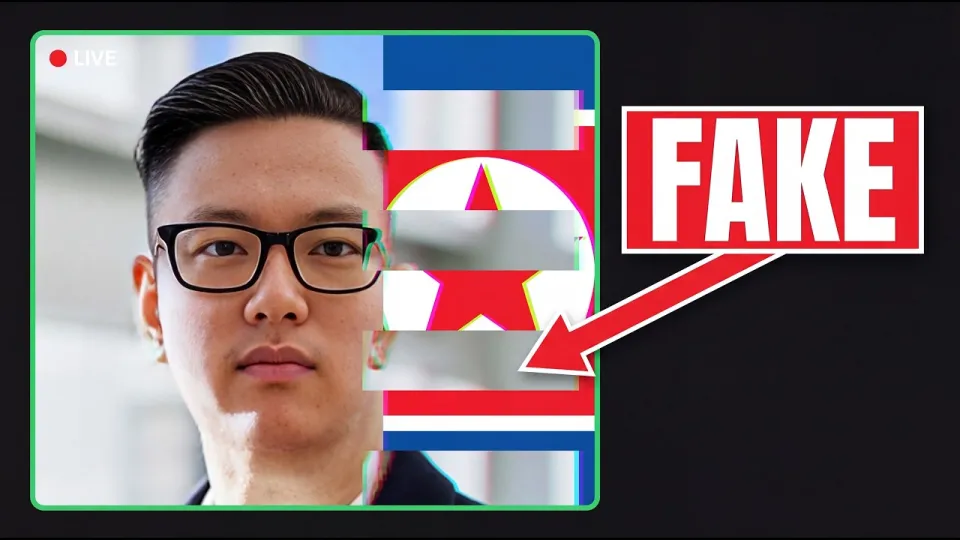
Video: Company Has No Idea Its New Hire Is a North Korean Hacker (crime story)
· based on the channel Max Crime
Key takeaways
- KnowBe4, a company that trains staff to spot fakes, hired a North Korean IT worker who passed four video interviews and a background check using an AI-altered photo and a real American's name.
- Christina Chapman of Arizona kept more than 90 work laptops on wire shelves in her home, each tagged with a company name and a stolen identity.
- Chapman was sentenced to 102 months in federal prison in July 2025; she kept about $177,000 while more than $17 million moved through her house.
- Microsoft Threat Intelligence tracks the DPRK IT-worker scheme as 'Jasper Sleet', and the FBI issued a public service announcement about it on 23 January 2025.
- The scheme is recruitment fraud rather than a network intrusion: the laptop arrives clean and starts loading malware once a real employee is at the keyboard.
A crime story is the better frame for the North Korean IT-worker scheme than a hacking story, because nothing in the typical case is broken into. The employer posts a remote job, interviews a fluent candidate on video, runs a background check that comes back clean and ships a laptop to an address in the United States. The fraud is in who is typing, not in how the network was breached — and that is why the crime story reads as recruitment fraud, identity theft and money laundering rather than as a data breach.
Why the crime story framing beats a hacking story here
The first sentence of the case is usually a surprise to the victim company: they were not hacked, they were hired. The candidate who passed four video interviews at the security-awareness firm KnowBe4 in 2024 used a stolen American identity, an AI-altered photo and a plausible work history, and the background check cleared because the name and documents belonged to a real person. Only when the company-issued laptop was handed over did the machine begin loading malware, which is what exposed the hire.
That sequence explains why the crime story is the more accurate label:
- The applicant never needs to defeat a firewall; he needs to defeat a hiring manager.
- The identity is real, so verification services return a pass.
- The malware arrives after onboarding, carried by the person the company itself let in.
- The money is laundered through U.S.-based intermediaries rather than stolen directly from the employer.
A hacking story would put the emphasis on tools and exploits. The crime story puts it on people, documents and addresses — and that is where the evidence actually lives.
What the laptop farm in Arizona actually was
A laptop farm is a room full of company-issued computers, each connected to the internet from a U.S. address so that the remote worker appears to be sitting in America. Christina Chapman, who lived in Arizona, kept more than 90 of these machines on wire shelves in her home, each tagged with the name of a company and a stolen identity, according to the Justice Department's account of the case. The machines were shipped to her address, set up on her network and kept running while the people actually doing the work sat thousands of miles away.
The financial picture is the part that makes the scale concrete. Chapman kept about $177,000 for herself, while more than $17 million passed through her house in the course of the scheme. She was sentenced in July 2025 to 102 months in federal prison. Her defense was that she did not know who she was really working for; prosecutors pointed to her own messages as evidence that she did.
How a North Korean IT worker passes a video interview
The interview stage is where the scheme is most exposed, so it is where the most preparation goes. Candidates use several overlapping techniques:
- Stolen identities. A real U.S. person's name, date of birth and documents are purchased or borrowed, so background checks confirm a human being who exists.
- Altered images. Profile photos are edited, sometimes with AI tools, so reverse-image searches do not match a known face.
- Intermediaries. A fluent English speaker may handle calls or sit in on interviews while the actual worker stays off camera.
- Remote infrastructure. The laptop farm supplies the U.S. IP address, so login logs and location checks look domestic.
KnowBe4 described the incident publicly in July 2024 and confirmed the hire was a North Korean IT worker; the company's own account notes that the fake employee's application photo was among the artifacts that later helped investigators. Microsoft Threat Intelligence, which tracks the broader campaign as "Jasper Sleet," published its analysis in June 2025, and the FBI's Internet Crime Complaint Center issued a public service announcement about DPRK IT workers on 23 January 2025.
What the money trail shows and where the rest went
The visible payment to the person on the ground is small next to the volume moving through the operation. Chapman's roughly $177,000 sits against more than $17 million that passed through her house, which means the bulk of the wages earned by the fake employees was routed onward — to handlers, to other accounts, and eventually toward the DPRK's weapons programs, according to U.S. authorities. The FBI and Justice Department have repeatedly described the IT-worker scheme as a revenue channel for North Korea, alongside cryptocurrency theft.
That gap is the open question in the case: the farm operator is the visible, prosecutable node, while the layers above her are dispersed. Federal cases have named facilitators and identified clusters of laptops in multiple states, but each seizure tends to reveal another set of addresses rather than the top of the structure.
How companies get caught and what the warning signs look like
A company usually discovers the problem after the laptop starts behaving oddly, not during hiring. In the KnowBe4 case, the machine began loading malware shortly after it was issued, and the company's own security team detected it — an irony worth noting, since KnowBe4 sells security-awareness training. Common red flags that surface in these cases include:
- A U.S. address that matches a residence already linked to multiple new hires.
- A candidate who insists on a specific laptop model or shipping route.
- Reluctance to appear on camera beyond short, scripted sessions.
- A background check that clears a name whose digital footprint does not match the résumé.
- Login patterns that come from one IP range across several supposedly unrelated employees.
The practical lesson for employers is that identity verification and device monitoring have to meet in the middle: the résumé check and the network check are looking at two halves of the same fraud.
Typical questions from viewers of the case
Viewers of the breakdown tend to ask the same things, and they are the right questions. Why would a company that trains people to spot fakes fall for one? Because the training is aimed at phishing emails, not at a fluent colleague with a valid identity. How does a background check pass? Because the identity is genuine — the fraud is in who is using it. Why ship laptops to a house? Because a U.S. IP address is the cheapest way to look local. And where did the rest of the money go? Upward, through accounts that the visible operator never controlled. None of these have a single clean answer, which is part of why the story keeps being retold.
Conclusion
The North Korean IT-worker scheme works because it inverts the usual security assumption: the threat is not a stranger breaking in but a colleague who was welcomed. Christina Chapman's laptop farm, the 102-month sentence, the roughly $177,000 she kept against more than $17 million that moved through her house, and KnowBe4's four-interview hire all describe the same mechanism — a real identity, a U.S. address and a company willing to trust both. Max Crime assembled the video breakdown from Justice Department releases, the FBI's public service announcement, Microsoft's "Jasper Sleet" reporting and KnowBe4's own account, and the case remains a useful test for any employer hiring remotely today.
Source: Company Has No Idea Its New Hire Is a North Korean Hacker (crime story) · Markdown version
Questions & answers
How did a North Korean IT worker pass a background check at a security company?
The candidate used a real American's name and documents, so verification services found a person who actually exists. The photo was altered with AI tools and the work history was plausible, which is why a company that trains staff to spot fakes still cleared the hire. The fraud only became visible when the issued laptop started loading malware.
What is a laptop farm and why is it needed?
A laptop farm is a collection of company-issued computers kept running from a U.S. address so that a remote worker appears to be in the country. Christina Chapman kept more than 90 machines on wire shelves in her Arizona home, each tagged with a company and a stolen identity. Without that local presence, login locations and shipping addresses would give the scheme away.
How much money did the scheme move and where did it go?
Chapman kept about $177,000, while more than $17 million passed through her house during the operation. U.S. authorities describe the IT-worker scheme as a revenue channel for North Korea, so most of the wages were routed onward through intermediaries rather than kept by the person operating the farm.
Would a normal company catch a hire like this?
Often not at the hiring stage, because the identity is genuine and the interview performance is prepared. Detection usually comes later, from device monitoring, from an address linked to multiple new hires, or from login patterns shared across supposedly unrelated employees. Combining identity checks with network monitoring is the practical defense.